Visual Privacy Program Game Plan
Originally published on LinkedIn in January 2017, as a follow-up to GDPR project considerations. The Visual Game Plan approach remains a practical tool for communicating any privacy or compliance programme to senior stakeholders.
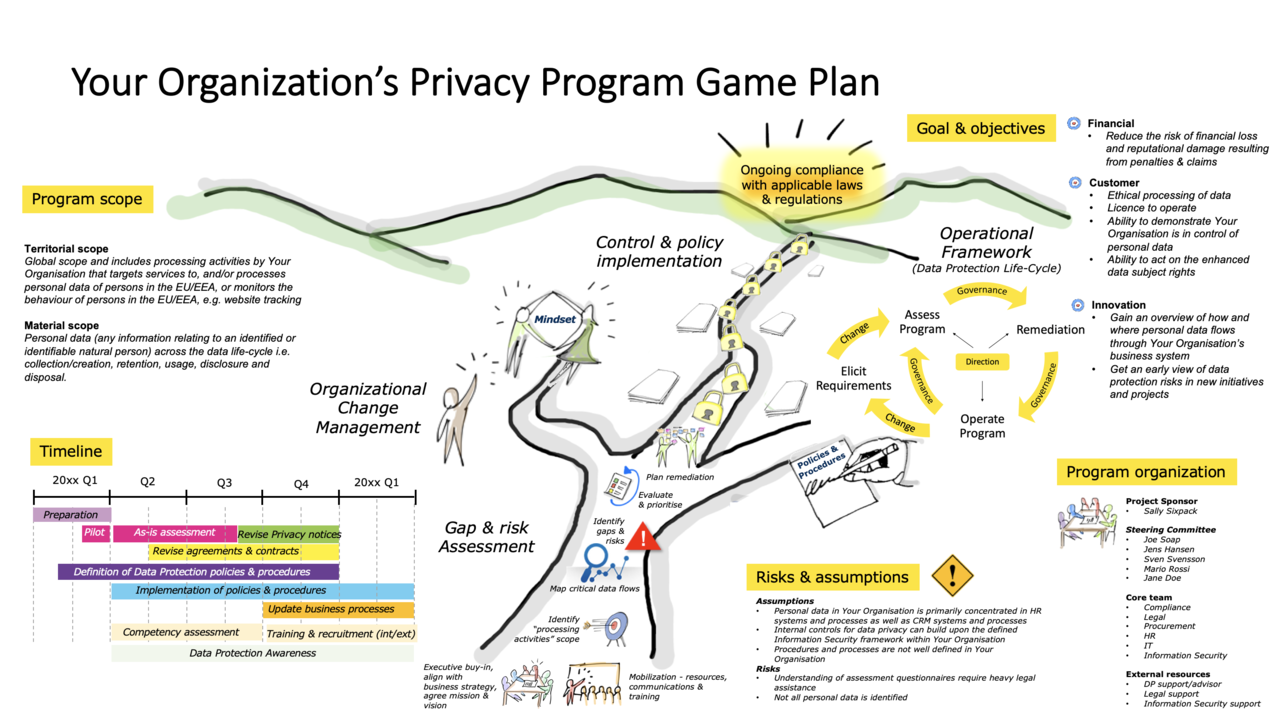
Once you have assembled a core team of subject matter experts (SMEs)* to help your Project or Programme Manager define how your organisation will tackle data protection legislation — and formulated this in a Project or Programme Initiation Document (PID) or Programme Charter — a Visual Game Plan is a useful tool both during and after that work.
What is a Visual Game Plan? #
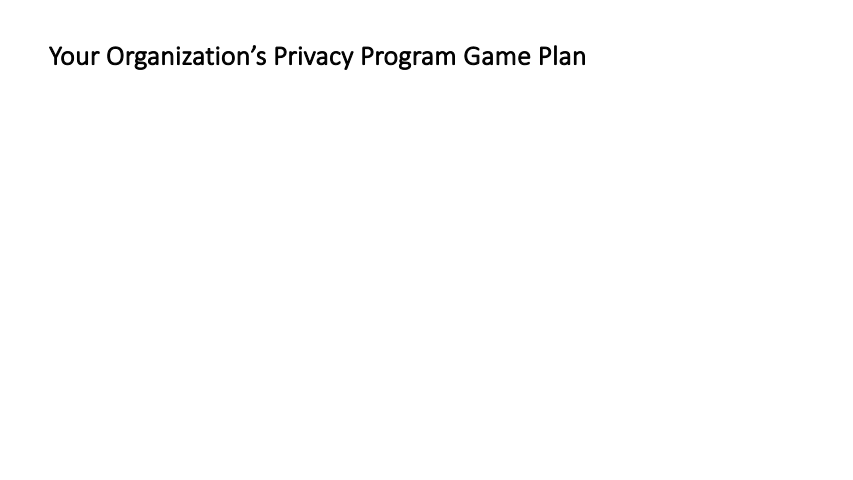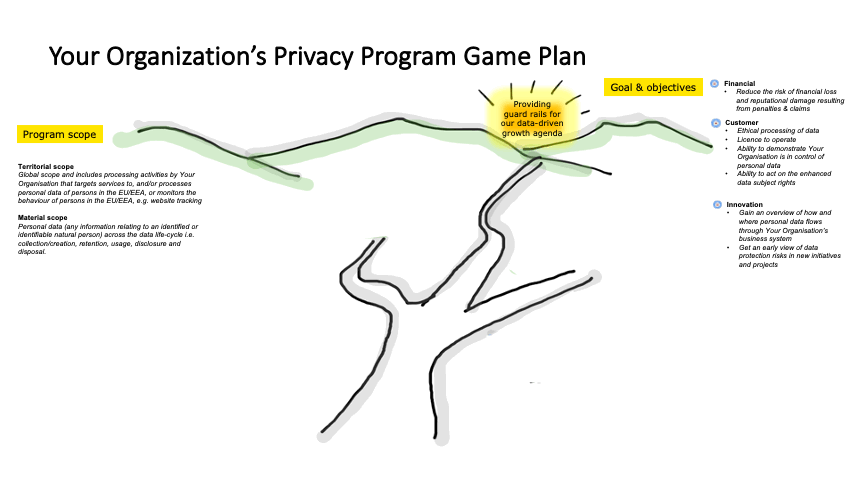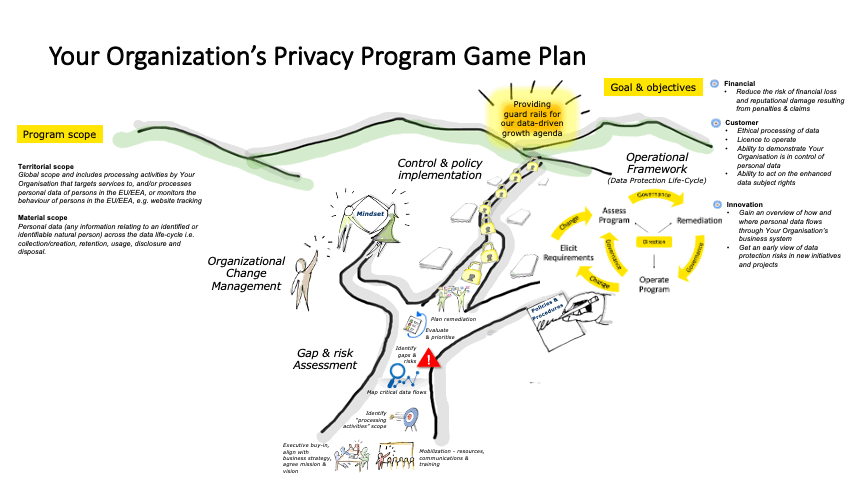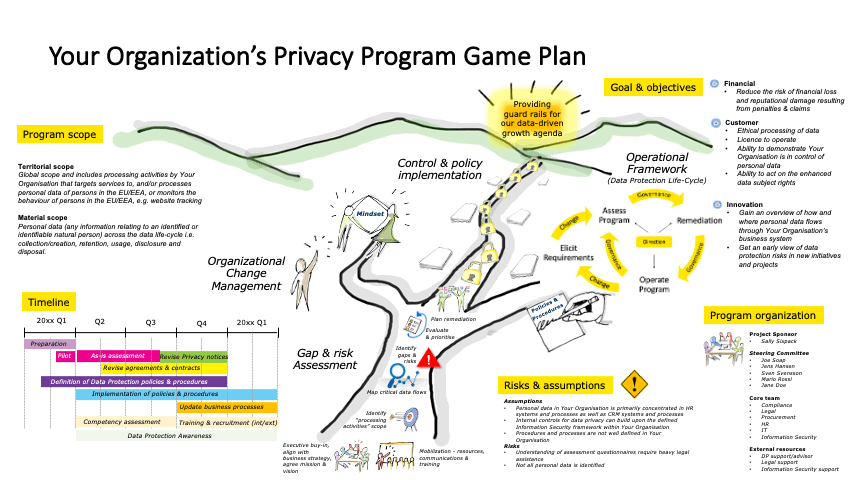
A Visual Game Plan is a one-page summary of your PID. It communicates your organisation’s data protection challenge to busy executives, senior managers, and anyone else who needs to understand the gist of your privacy programme in about ten minutes.
The document is simple, easy to digest, and visually tells the key elements of your “data protection story”. If presenting using PowerPoint, Keynote, or a similar tool, introduce each element one by one using the animation function.
What to include #
Typical elements to consider for your Visual Game Plan:
- Goal and objectives
- Scope
- Approach
- Key resources
- Key risks
- Key assumptions
- Known issues
- Known dependencies
- Rough timeline
- Ballpark budget
The Visual Game Plan can be drawn up on flip chart paper or as a PowerPoint slide. Once you have presented it and addressed any questions, modify it as needed — for example, with additional risks — and then circulate it to your audience together with the full PID or Charter.
Incidentally, Visual Game Plans came to me via David Sibbet in his book Visual Meetings — very inspirational.
Frequently Asked Questions #
What is a Visual Privacy Program Game Plan? A Visual Game Plan is a one-page summary of your data protection programme, covering scope, objectives, approach, key risks, and timeline. It is designed to brief busy executives and senior stakeholders on your GDPR or privacy programme in approximately ten minutes.
What should a Visual Game Plan include? At a minimum: goal and objectives, programme scope, the approach you are taking, key resources, key risks and assumptions, known issues and dependencies, a rough timeline, and an indicative budget. The exact content will vary depending on your organisation’s situation.
How is a Visual Game Plan different from a Project Initiation Document? A PID or Programme Charter is a detailed, multi-page document covering the why, what, when, who, and how of your programme. The Visual Game Plan is a one-page summary designed to communicate the essence quickly and clearly to stakeholders who will not read the full PID.
* Suggested SMEs to involve from the outset: Legal, IT, HR, Compliance, Information Security, Risk Management, Internal Audit, Procurement, and your lines of business.
I publish a fortnightly newsletter on data protection and privacy — practical, opinionated, and free. You can sign up on the newsletter page.